
Vendor contract review for self-hosted teams
Review a vendor agreement against the policies you already keep. GRCompliance can flag clauses and suggest wording. A person still decides what to accept. The review runs on the instance you host.
Automated Redlining & Clause Intelligence
Instant
Agreement Validation
Map contract clauses to the security and compliance policies you already keep. The software does not decide which terms you accept.
Keep the source file, the reviewer, and the decision. A flagged clause is a prompt for a person, not a completed review.
Smart Contract
Analysis Engine
Advanced AI that understands legal language, identifies risky clauses, and generates compliant redlines in seconds.
AI Clause Analysis
Looks for clause types such as liability, indemnity, service levels, and data processing terms.
- Liability, indemnity, and data-processing clauses
- Risk scoring per clause
- Industry benchmark comparison
Automated Redlining
AI generates suggested redlines that align vendor terms with your organization's acceptable risk thresholds.
- One-click acceptance
- Custom template library
- Version control & history
Policy Mapping
Automatically map contract clauses to ISO 27001, SOC 2, GDPR, and custom policy controls.
- Auto-control linking
- Compliance gap alerts
- Evidence attachment
Vendor Risk Scoring
Quantified vendor risk scores based on contract terms, security posture, and breach history.
- 0-100 risk score
- Historical trending
- Tier classification
Policy Translation
Generate compliance policies in multiple languages for global organizations
Enterprise Security
You host the instance. Encryption at rest depends on the disk you provide.
Real-Time Processing
Analyze 100+ page contracts in under 30 seconds
The Vendor
Review Engine
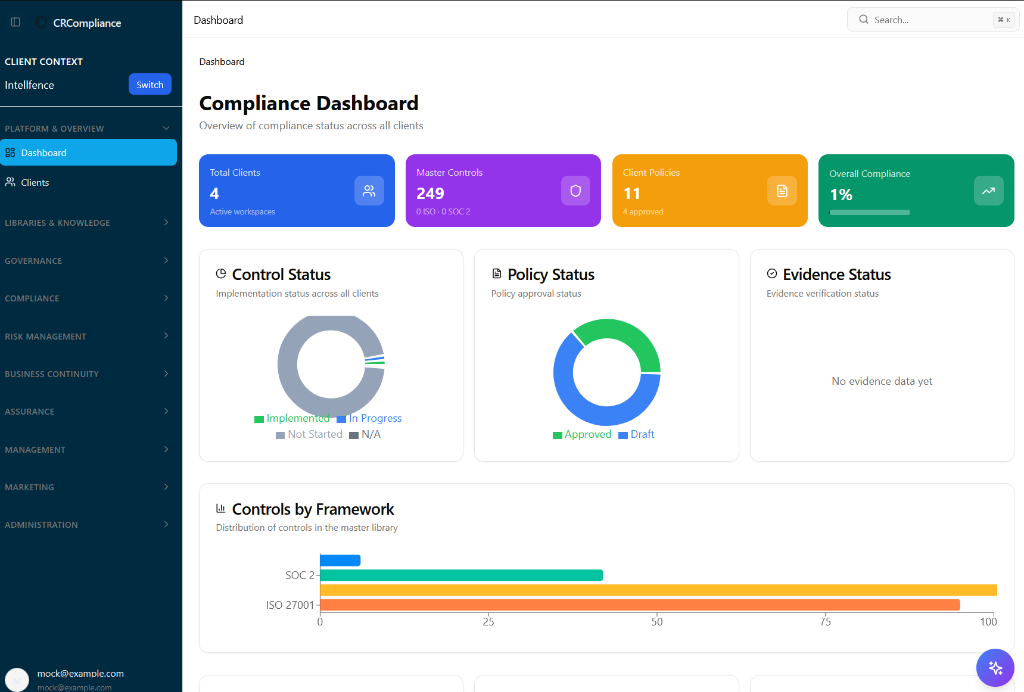
01. Supply Chain Pulse
A command-level dashboard for tracking 4th-party ecosystem exposure. Monitor Dark Web leaks and potential breaches across your entire vendor hierarchy in one view.
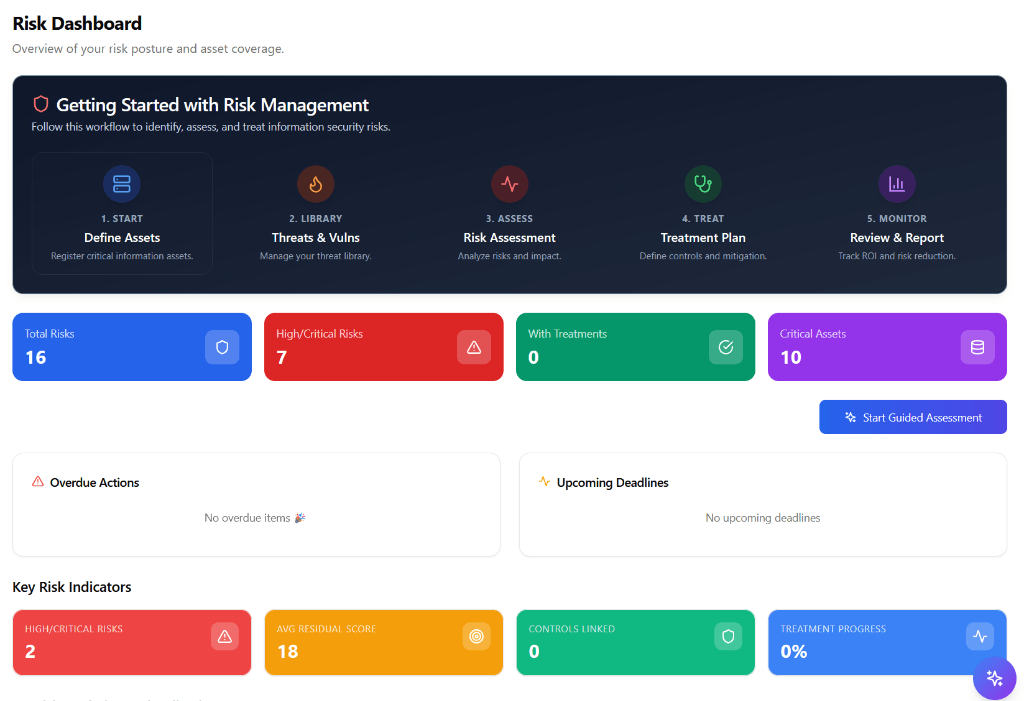
02. Unified Registry
One definitive list of active vendors. Categorize by risk level, track trust scores, and manage subprocessor onboarding through a high-frequency, actionable registry interface.
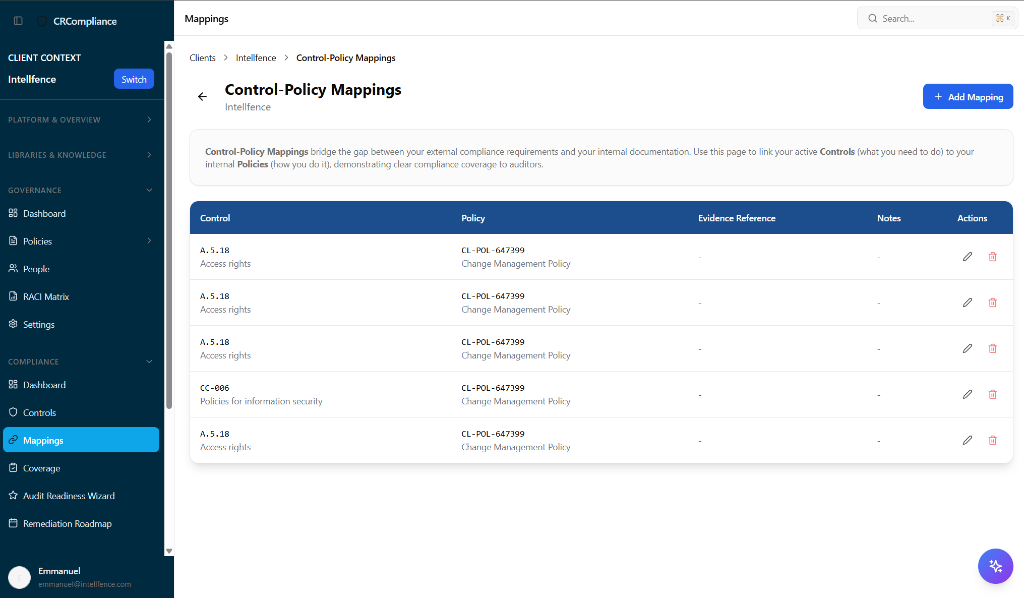
03. Response Velocity
Track inbound and outbound security questionnaires (SIG, CAIQ, SOC2). Move vendors from 'Draft' to 'Completed' in record time with automated evidence mapping.
Risk Clause
Scanner
Instantly flag unfavorable liability, indemnity, or SLA terms that violate your corporate risk tolerance. Zero manual scanning required.
Policy
Alignment
Ensure every Vendor Agreement and DPA matches your ISO/SOC2/GDPR policies. Our agent compares the contract to your live control library.
Automated
Redlining
Don't just find problems. Fix them. Our agent generates redlined versions of contracts that normalize vendor terms to your standards.
Unblock
Onboarding.
Review the agreement on the instance you host, then send the decision to the person who can sign it.
Onboarding Automation Module arriving Q2 2026